See the output before you install anything.
At the end of an engagement, SegAudit exports every client deliverable as one .zip. The examples on this page come from Northline Process, the sample engagement that ships with the product: three plants in Tulsa, Fresno and Savannah with different addressing and the same zone and rule names.
What is in the pack, and who reads it
Each deliverable is written for a specific reader. The same evidence feeds all of them, so the brief, the change package and the crosswalk never disagree. Every document comes in Word and markdown, and every table opens in Excel.
For the plant manager, CISO and board
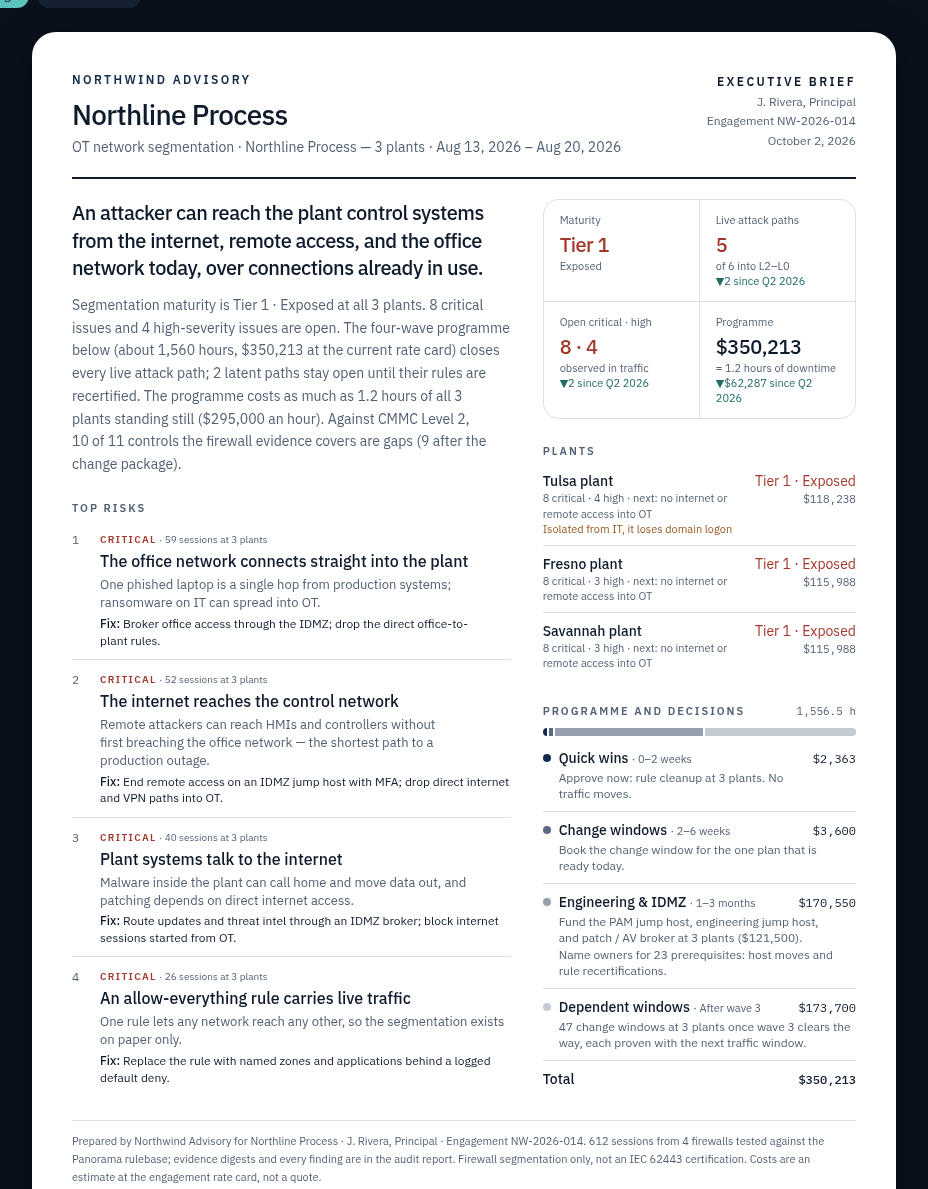
Executive brief
One page for the plant manager, CISO or board: can an attacker reach the control systems today, from where, and what it costs to close.
One brief per plant
When the engagement covers several plants, each plant manager gets the same page for their own site.
Remediation roadmap
Every change plan in waves, priced from your rate card, with the business case against downtime.
Proposal
The statement of work for the follow-on engagement, phased to match the roadmap.
For the firewall engineer and the CAB
Firewall change package
Every rule change the plans need, ready for change management, with a risk rating, verification and rollback for each.
CLI in one file
The commands in package order, for the engineer who will paste them.
Change register and tickets
One row per change for the change-management tool, and tickets ready for Jira or ServiceNow.
Firewall rule review
Every allow rule that touches OT with a recommendation and space for the owner's sign-off.
For auditors and compliance
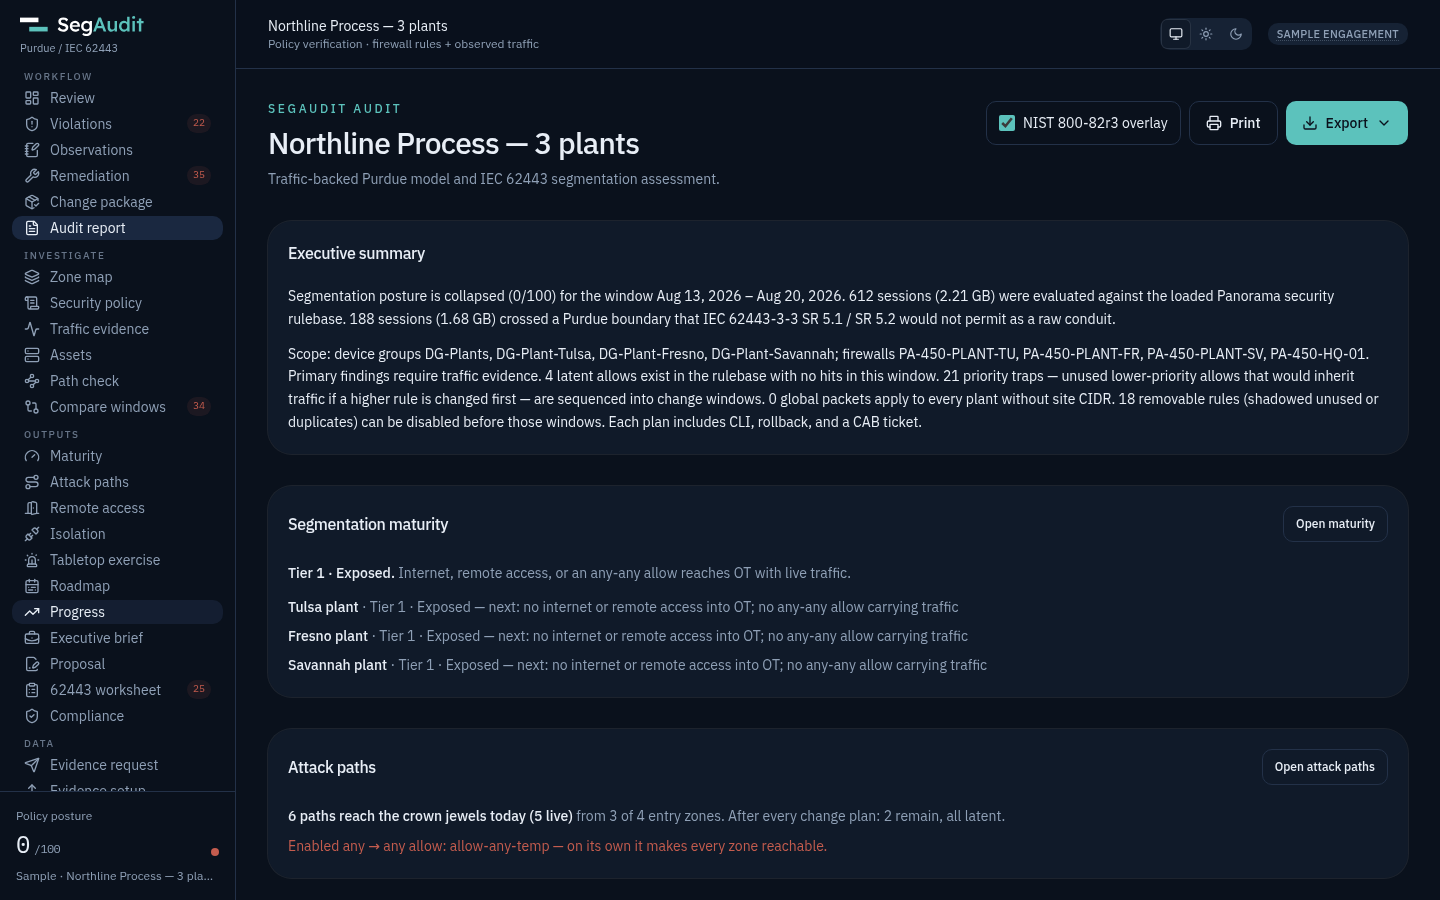
Audit report
Findings, evidence, maturity, attack paths, remote access, assets and method, with the chain of custody.
Findings
Every finding as a spreadsheet to sort and filter.
IEC 62443-3-2 worksheet
Each observed conduit with its target security level and the proposed fix.
Compliance crosswalk
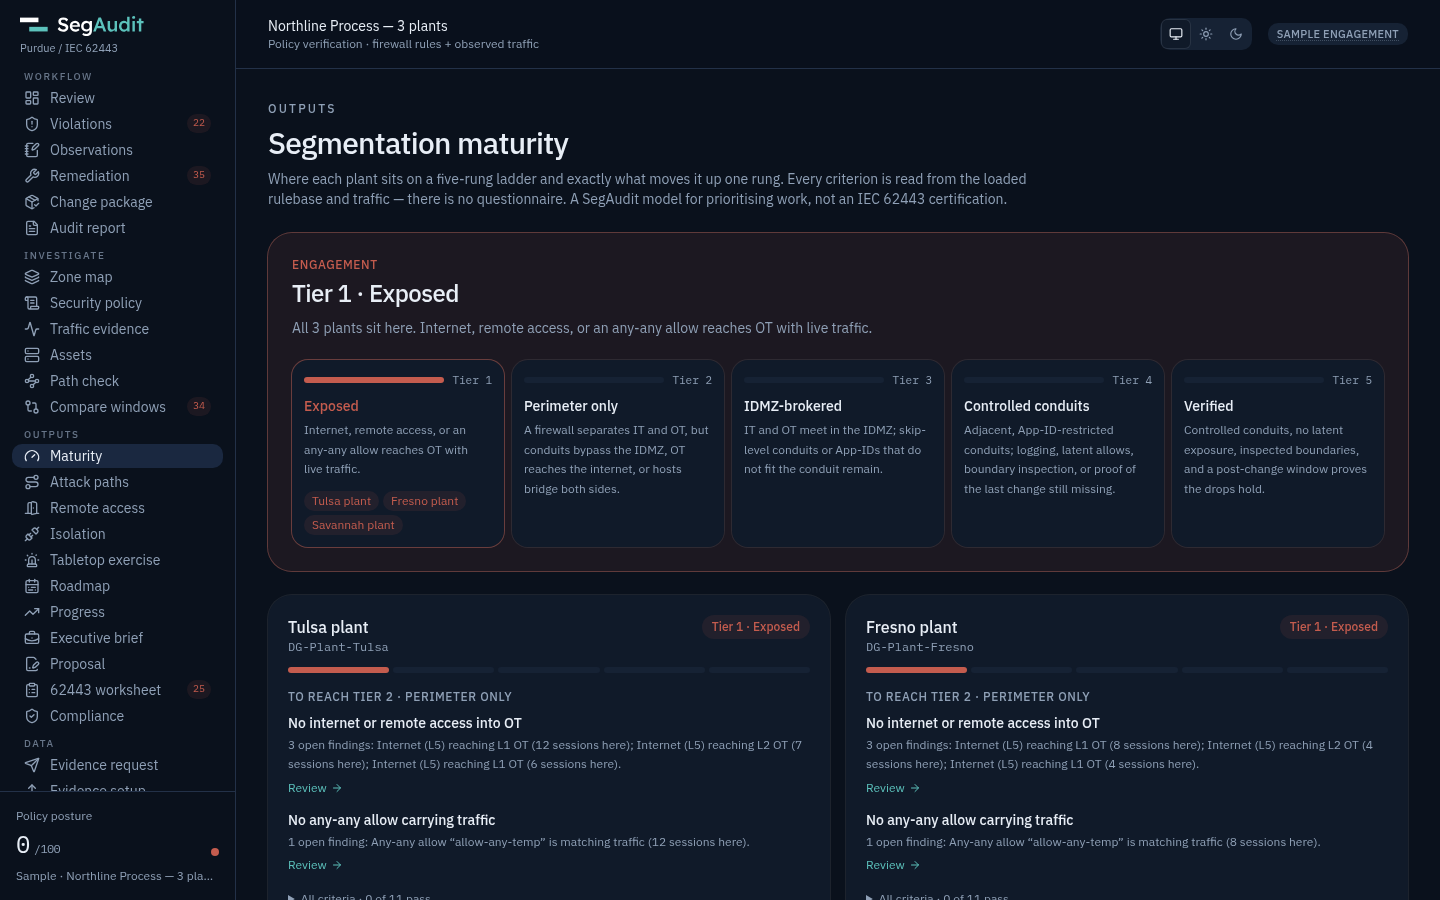
Where the client stands against IEC 62443, NIST CSF, CMMC, ISO 27001, NIS2 and their sector framework, before and after the change package.
Asset inventory
Every address as an asset with its role, criticality and exposure.
For security operations and incident response
SOC detections
What the SOC should alert on once the change package is in.
Remote access inventory
Every way into OT from outside, and what to do about it.
Isolation runbook
Per plant, what stops when OT is cut off from IT and how to prepare.
Tabletop exercise
A ransomware scenario on the client's own paths, ready to facilitate.
A look inside
Two excerpts from the Northline pack. The rest of each opens in the product.
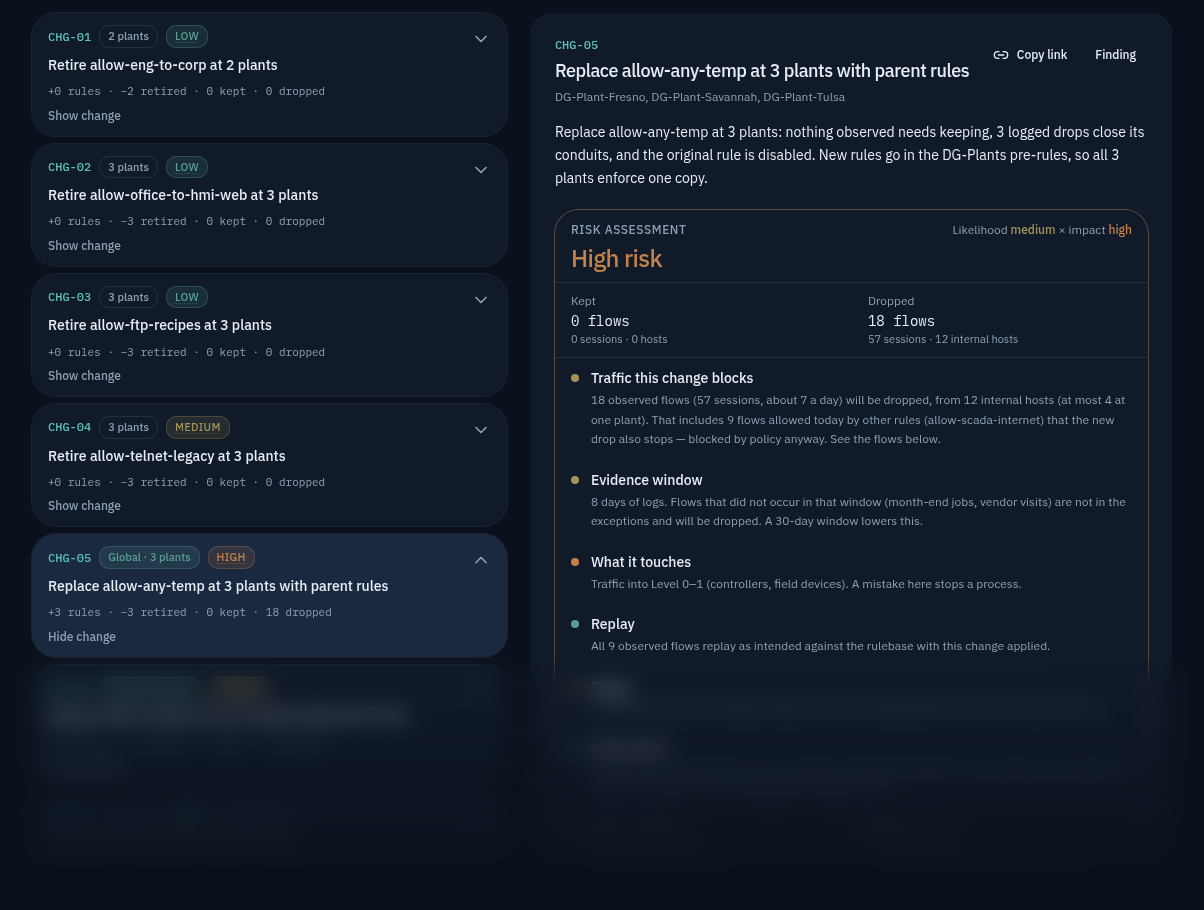 Pre-checks, commands, verification and rollback for every change are in the product
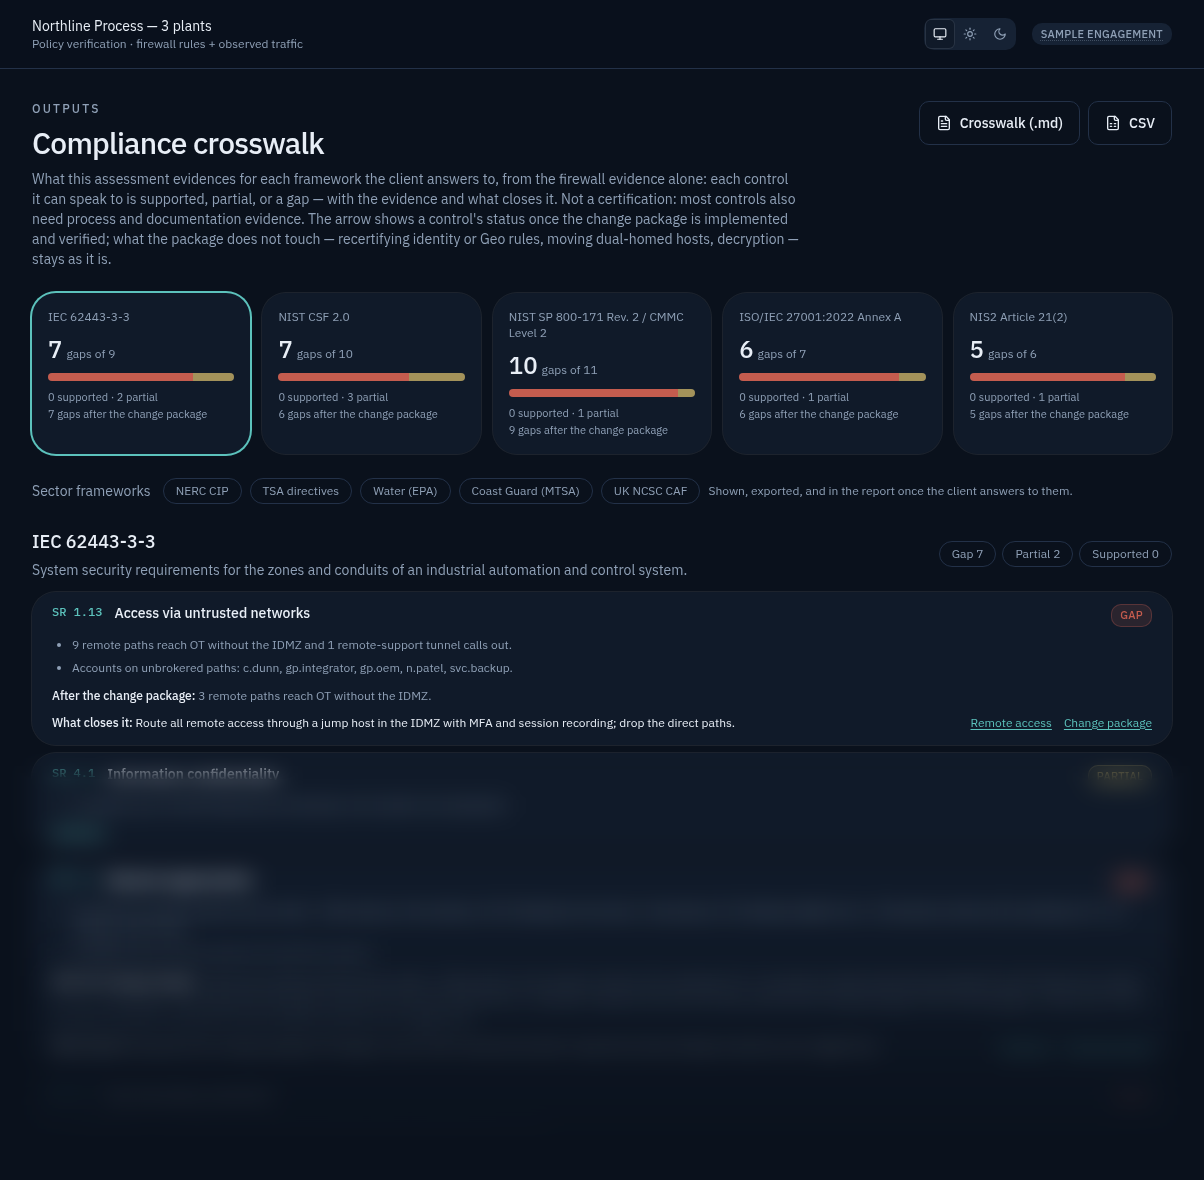 Every control, with its evidence and what closes it, is in the product
How the pack is put together
- One folder per client and dayEvery file sits in a folder named after the client and the date, numbered in reading order.
- A README with the evidence hashesIt lists each file with a one-line description and the SHA-256 of the config and traffic log the results came from.
- Word and markdownEvery document is in the pack twice: a .docx in Word's own styles, so your firm's template restyles it, and the .md for email and version control. Your logo and letterhead head every Word page.
- Opens in the tools people already useCSVs open in Excel as UTF-8, and the change tickets import into Jira or ServiceNow.
- Password-protected if the client asksExport the same pack as an AES-256 zip. 7-Zip, WinZip, Keka and Windows 11's File Explorer open it; file names stay visible, contents do not.
- Prints as designedThe executive brief prints on one Letter or A4 page and the proposal prints from its page. The audit report prints dark on white whatever the screen theme.
- Your letterheadSet your firm, logo, rate card and proposal terms once in the firm profile. The brief, report, roadmap and proposal carry them.
- Only what the evidence supportsA file appears when the evidence has something for it. With no change plans there is no roadmap, and with one plant there are no per-plant briefs.
See the whole pack
A free Professional trial opens the complete Northline pack and runs the same analysis on your own evidence. Open the sample, go to Audit report, and choose Export, then All deliverables (.zip). Trial deliverables are marked TRIAL. The first audit guide walks the sample screen by screen.
Questions about the deliverables
Why are parts of this page blurred?
The pages above are excerpts. The full change package, every control in the crosswalk and the rest of the pack open in the product, on the sample engagement and on your own evidence.
Is the pack a set of PDFs?
No. The pack holds Word, markdown and CSV files so you and the client can edit, import and file them. The brief, proposal and audit report also print to paper or PDF from the browser.
Does it contain the client's firewall config?
No. The running config and traffic log are not in the pack, only their SHA-256. The findings do name rules, zones and host addresses, so treat the pack as confidential client material.
Can the client check where the results came from?
Yes. The README and the audit report carry the SHA-256 of each evidence file, and the evidence request asks the client's engineer for the same hashes when they send the files.
Is the compliance crosswalk a certification?
No. It is evidence toward each framework from the firewall's point of view. What the product drafts, such as the asset inventory, counts as partial until the client confirms it.