Findings in the language your auditors use.
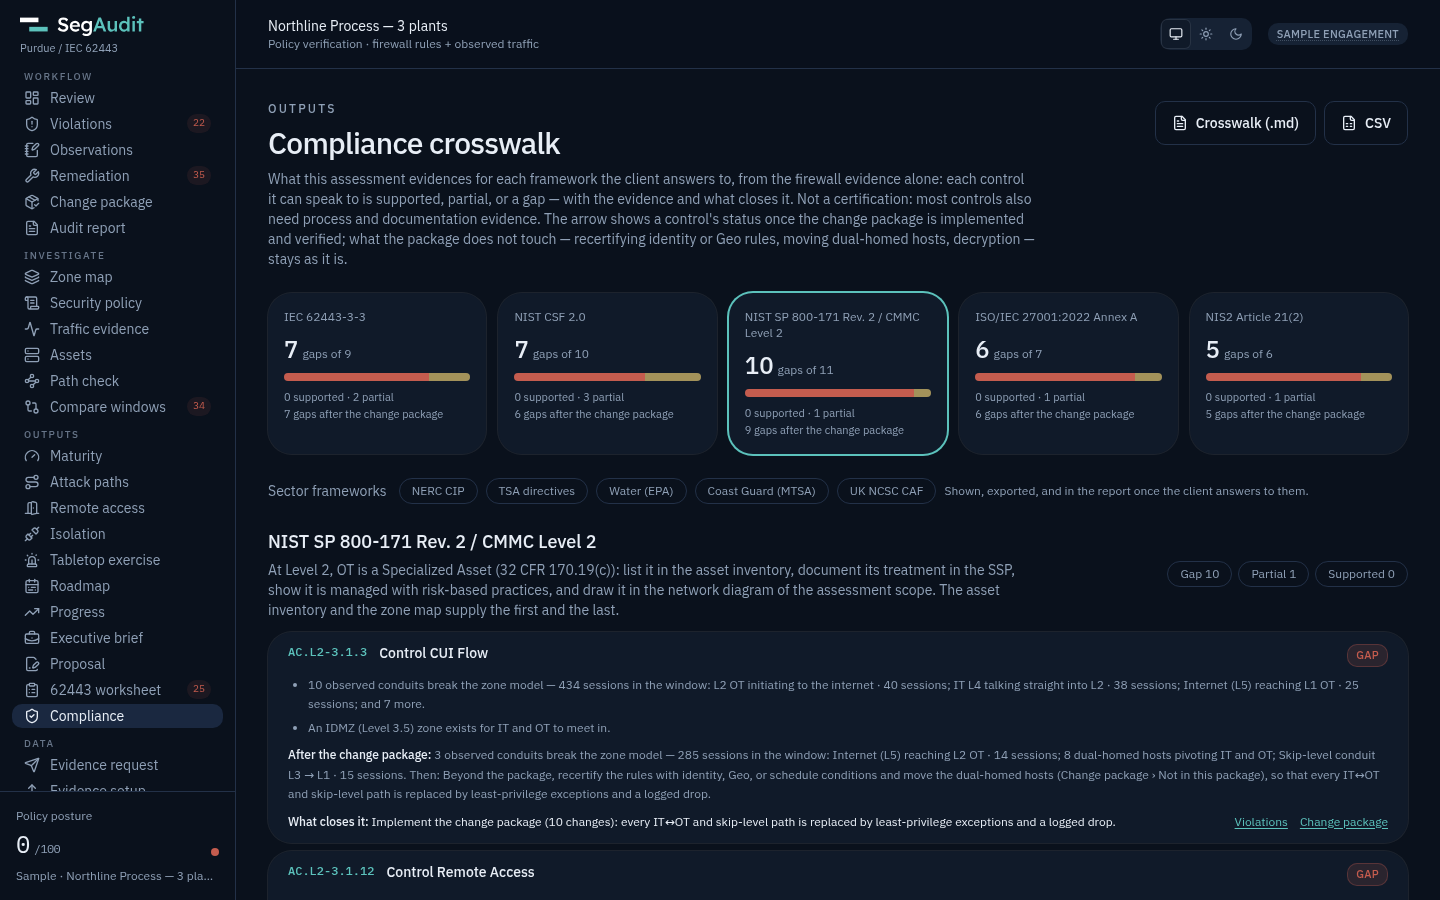
The question after every segmentation assessment is what it means for the framework the plant answers to. SegAudit answers it control by control, from the same firewall evidence as the findings, and says what closes each gap.
How a control is judged
Each control the firewall evidence can speak to gets one of three verdicts, with the evidence behind it.
Supported
The firewall evidence supports the control. The crosswalk shows the evidence behind the verdict.
Partial
Some evidence is there, or it comes from something the tool drafted, such as the asset inventory or the conduit worksheet, which the client still has to confirm and maintain.
Gap
The evidence shows the control is not met. Each gap says what closes it and links to the change package, remote access review or asset inventory.
Controls in the crosswalk
| Framework | Controls judged from the evidence |
|---|---|
| IEC 62443-3-3 | 9 controls |
| NIST CSF 2.0 | 10 controls |
| NIST SP 800-171 Rev. 2 / CMMC Level 2 | 11 controls |
| ISO/IEC 27001:2022 Annex A | 7 controls |
| NIS2 Article 21(2) | 6 controls |
The control-by-control list for each framework is in the customer guides.
Sector frameworks
Five sector and national rules, judged from the same evidence with the status after the change package.
| Framework | Who it applies to | Controls judged from the evidence |
|---|---|---|
| NERC CIP-005-7 / CIP-007-6 | Electric utilities | 10 controls |
| TSA security directives | Pipelines (SD Pipeline-2021-02G) and rail (SD 1580/82-2022-01E) | 5 controls |
| EPA water checklist | Drinking water and wastewater systems | 11 controls |
| US Coast Guard, 33 CFR 101.650 | Ports, terminals, vessels and offshore facilities | 11 controls |
| UK NCSC CAF 4.0 | UK operators of essential services | 9 controls |
Only when the client answers to it
Sector frameworks stay off the Compliance page, the report and the deliverables pack until you turn one on for the client, on the Compliance page, under the letterhead or as a firm profile default.
NERC CIP reads the zone model
OT zones are read as the Electronic Security Perimeter and the firewall at their boundary as its Electronic Access Points. CIP-007 R1.1 is partial at best, because listening ports are a host check.
TSA segmentation uses isolation readiness
The directives ask that OT keeps running if IT is compromised. The isolation readiness of each plant is the evidence.
Dates that matter
Coast Guard segmentation is due on 16 July 2027. CIP-005-8 and CIP-007-7.1 take effect on 1 July 2028. Confirm the versions in force for the audit period.
Beyond the crosswalk
IEC 62443-3-2 worksheet
Each observed conduit with its zones, target security level, the traffic behind it and the proposed fix. Export it as markdown or CSV.
Purdue model
Every zone is mapped to L0 to L5 or the L3.5 IDMZ, and traffic the model does not allow becomes a finding.
App-ID matrix (SR 5.3)
Expected and restricted applications for each hop, editable per engagement.
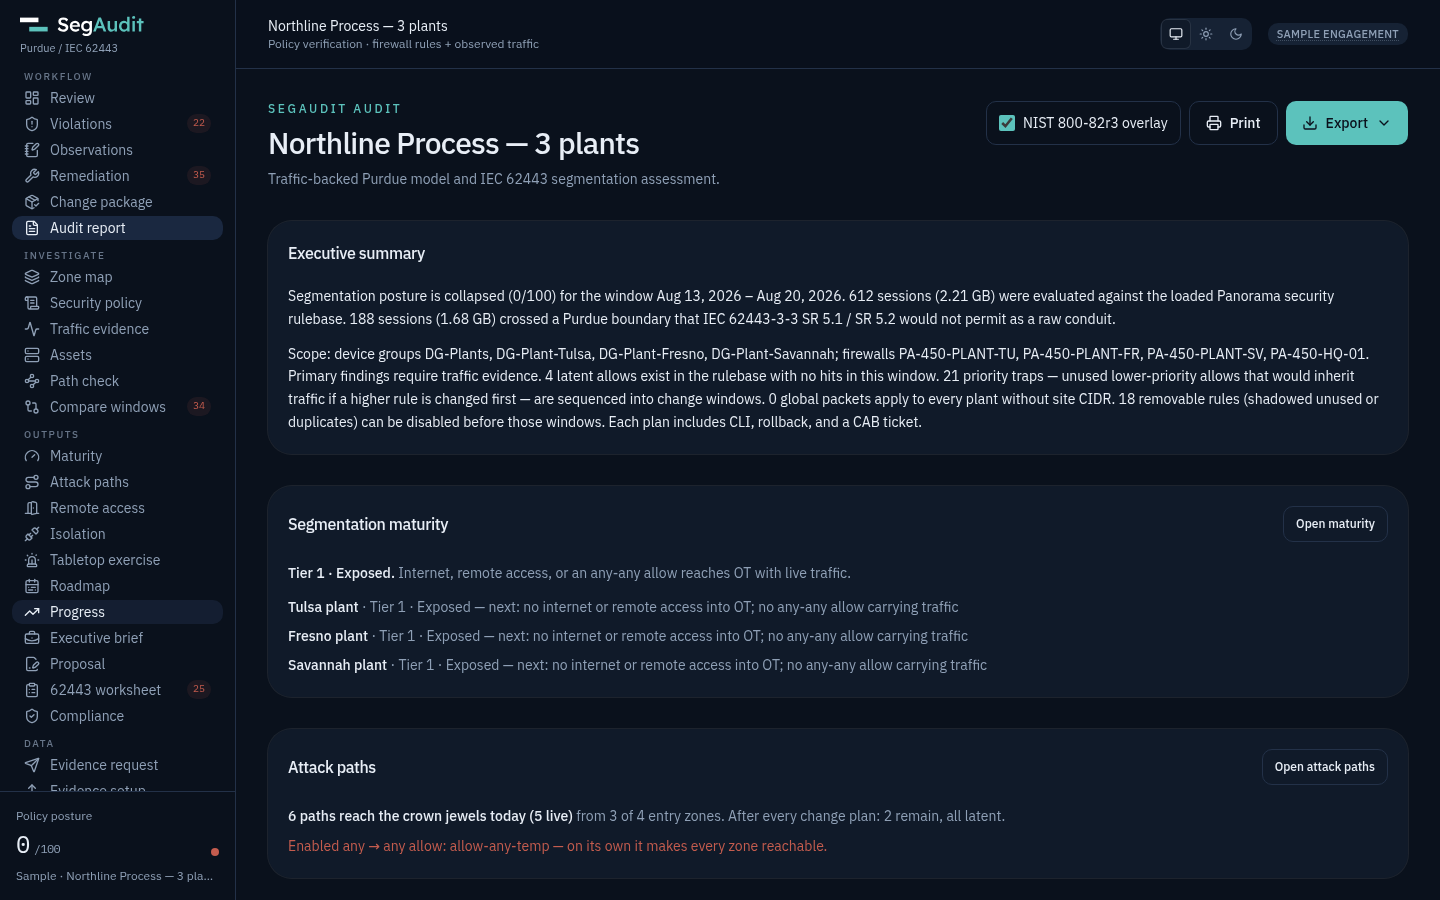
NIST SP 800-82r3 overlay
The audit report can restate each finding in SP 800-82r3 terms, such as SC-7 boundary protection and AC-4 information flow enforcement. Untick it for an IEC-only report.
MITRE ATT&CK for ICS
Each technique the evidence leaves open, in attack order, with the evidence and the fix. Only techniques a rulebase and its traffic can speak to are listed.
CMMC Specialized Assets
At Level 2, OT is a Specialized Asset under 32 CFR 170.19(c). The asset inventory and the zone map supply two of the four things an assessor looks for.
What it does not claim
- Not a certificationSegAudit helps you assess segmentation controls. It does not certify compliance with any framework.
- Firewall evidence onlyMost controls also need process and documentation evidence that a firewall config and traffic log cannot provide.
- Some controls need Device-IDControls marked * are judged only when Device-ID reports operating systems, so an end-of-support OS can be spotted.
- Drafts stay partialAnything the tool drafts for the client counts as partial, never supported, until the client confirms it.
- Your observations count against itAn observation you record on a control holds it at partial, or gap when it is critical or high. The change package does not close it.
Common questions
Can the client's framework come first?
Yes. Pick the frameworks the client answers to when you fill in the letterhead, or set your usual ones in the firm profile. The executive brief summarizes where they stand against each, the crosswalk lists them first, and the report leads with them.
Does it show the effect of the fix?
Yes. Each control also shows its status once the change package is implemented and verified, and why, so you can see which gaps the package closes and which need more work.
Can we track it over time?
Recording a checkpoint at the end of each assessment freezes the gaps in every framework, so the next quarter shows movement in the client's own framework.
How do I get it out?
Export the crosswalk as markdown or CSV from its page. The audit report carries a summary, and the deliverables pack includes it in Word, markdown and CSV.
See how consultants and plant teams use the crosswalk, or read about the company's own status in the trust center.